C-SIX SENTINEL.AI
Next-Generation Threat Intelligence Platform
Enterprise SIEM & Autonomous SOC Solution
|
< 5 Seconds Detection & Response |
100% Autonomous |
Fixed Pricing OPEX/CAPEX |
Universal All Industries |
From Passive Monitoring to Active Defense.
Enterprise-Grade Protection 24/7.
Trusted by Hospitals | Universities | E-Commerce | Hosting Providers | Enterprises
C-SIX Sentinel.AI is an enterprise-grade Security Information and Event Management (SIEM) and Threat
Intelligence platform designed to deliver proactive and comprehensive protection across all industry sectors.
By combining advanced Machine Learning analytics with Generative AI capabilities, Sentinel transforms network security from passive monitoring into an Active Defense architecture. The platform detects,
analyzes, and automatically executes threat mitigation in seconds—without overwhelming your Security Operations Center team.
SECTOR |
APPLICATION & BENEFITS |
|---|---|
| Healthcare | Protects patient data and electronic medical records. Ensures HIPAA and UU PDP compliance. Prevents ransomware attacks that can disrupt critical medical services. |
| Education | Protects research intellectual property and student data. Secures academic systems against sabotage. Maintains security compliance for institutional accreditation. |
| E-Commerce | Protects payment transactions and customer data. Ensures PCI-DSS compliance. Prevents credential stuffing and account takeover attacks. |
| ISP/Hosting | Protects multi-tenant infrastructure. Isolates and monitors traffic between customer accounts. Provides active threat intelligence API to customers. |
| Enterprise | Protects global branch offices across multiple regions. Synchronizes threat intelligence to regional gateways. Centralizes monitoring and management. |
Core Enterprise Features
Active Threat Intelligence Feed API
ransforms Sentinel from a monitoring tool into a command center that distributes threat intelligence throughout your network infrastructure.
- Automated Blacklist Sync: Real-time API endpoint exports attacker IP addresses automatically
- Agnostic Device Compatibility: Works with MikroTik RouterOS, Linux IPTables, FortiGate, NGINX WAF using industry-standard formats
- Borderless Scalability: Distributes security rules across dozens of routers and servers in multiple branch offices and data centers
AI Forensic Copilot
ransforms raw telemetry logs into actionable cybersecurity intelligence through advanced language model analysis.
- Contextual Threat Analysis: Automatically dissects attack payloads with plain-language forensicexplanations
- Ready-to-Use Mitigation: Generates executable mitigation commands that operators can deploy immediately
- Dynamic Model Switching: Seamlessly switch between AI models through the user interface to maintain future-proof capabilities
Machine Learning Anomaly Detection
Behavioral analytics system that identifies zero-day threats bypassing traditional firewall signatures.
- Heuristic & Entropy Scoring: Calculates traffic deviations and payload complexity to detect previously unseen attack patterns
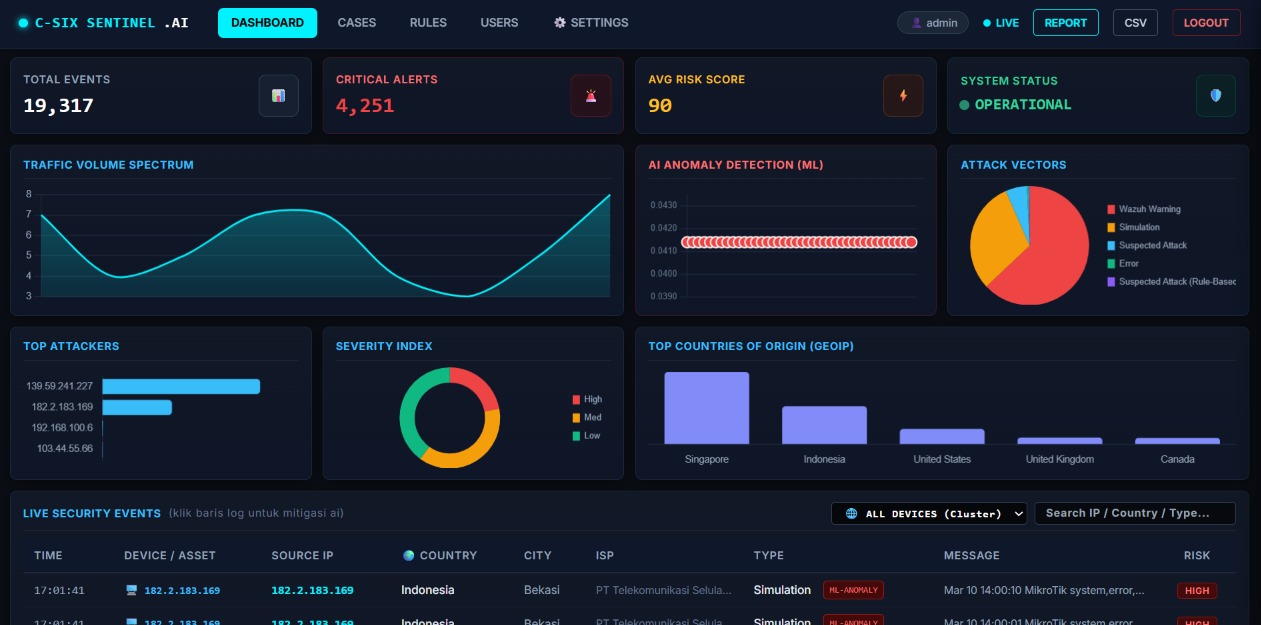
- Dynamic Threat Visualization: Real-time interactive visualization adapts to threat variations organically
Mini-SOAR Incident Case Management
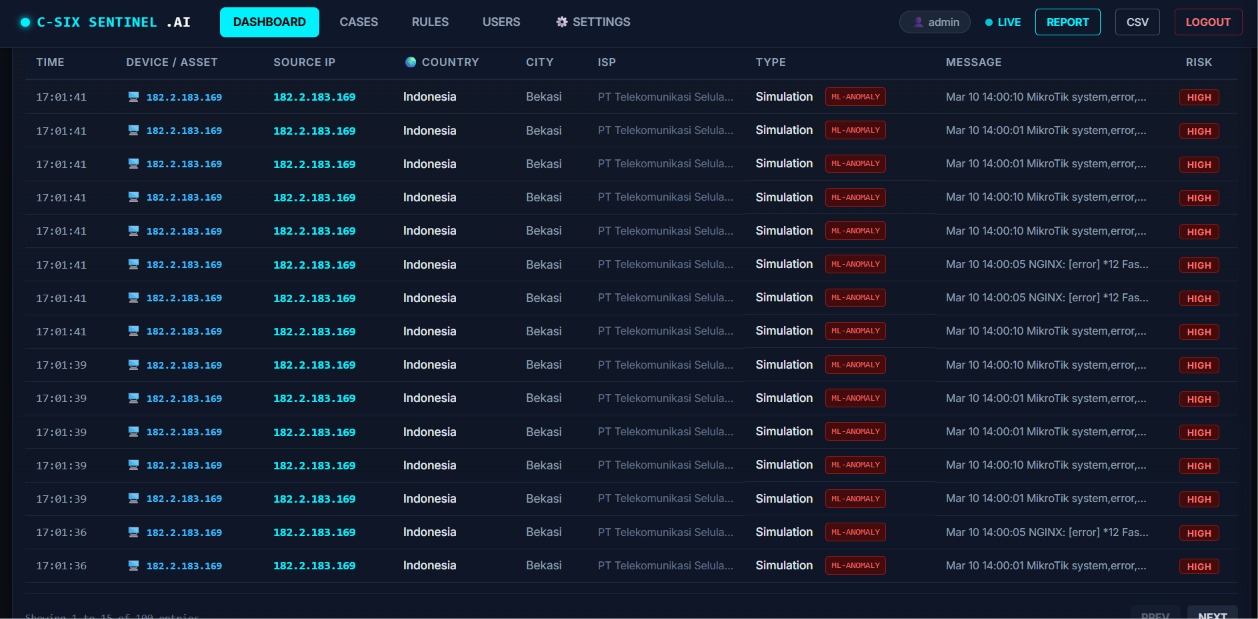
Intelligent aggregation system that eliminates alert fatigue by consolidating duplicate attack alerts.
- Intelligent Log Aggregation: Consolidates thousands of repeated attacks from the same source into a single case ticket
- Lifecycle Management: Track incident responses from OPEN through RESOLVED status for compliance audit trails
Autonomous 24/7 Alerting
Always-on notification system maintaining security posture without requiring constant team presence.
- Instant Telemetry Routing: Delivers high-risk incidents to mobile devices via Telegram in under 2 seconds
- Encrypted Email Notifications: Sends structured HTML alerts directly to corporate email with end-to-end
encryption
Unified SaaS Dashboard
Modern web interface providing comprehensive high-level security visibility and control.
- Global Threat Map: Visualizes attacker geographic origins by country, city, and ISP
- Centralized Credential Vault: All API keys and sensitive configuration stored in encrypted local database
Compliance & Business Continuity
Regulatory Compliance
Sentinel maintains comprehensive audit logs capturing every anomaly, penetration attempt, and operator response. These records export as structured reports required by ISO 27001, SOC2, and external auditors.
The platform provides concrete digital evidence demonstrating your organization’s security posture to regulators and compliance teams.
Data Protection Compliance
The platform minimizes data breach risk by identifying and blocking exploitation attempts at the network edge before they reach sensitive systems.
Comprehensive forensic logs accelerate incident investigation and response, supporting compliance with data protection regulations including UU PDP and GDPR notification requirements.
Predictable Budget Planning
Unlike traditional SIEM solutions with variable costs based on data volume processed, Sentinel operates on a fixed Enterprise Flat-Rate model.
This enables precise IT budget forecasting and eliminates unexpected cost
System Architecture
Data Ingestion Layer
CHANNEL |
SPECIFICATION |
|---|---|
| Syslog Bridge (UDP 514) | Raw log collection from network infrastructure. Automatic BSD/RFC 3164 header parsing. No agent installation required. Support for MikroTik, Cisco, Juniper, Fortigate, and other vendors. |
| Structured API (JSON Port 8081) |
REST endpoint for structured log data. Integration with Wazuh Manager and endpoint agents. Support for Windows, Linux, and macOS. Advanced normalization and data enrichment. |
Processing & Intelligence Layer
- Log Parser & Normalizer: Standardizes formats from diverse sources
- AI Forensic Analysis: LLM-powered contextual threat understanding
- ML Anomaly Detection: Isolation Forest algorithm for zero-day identification
- Risk Assessment: Classifies incidents as LOW, MEDIUM, or HIGH priority
Incident Orchestration Layer
- Case Manager: Aggregates related alerts into consolidated cases
- Active Threat Intelligence API: Distributes blacklists to firewalls and routers
- Automated Alerting: Multi-channel notification delivery
- Long-term Archive: Searchable log database with query interface
System Requirements
Server Specifications
COMPONENT |
REQUIREMENT |
|---|---|
| Operating System | Raw log collection from network infrastructure. Automatic BSD/RFC 3164 header parsing. No agent installation required. Support for MikroTik, Cisco, Juniper, Fortigate, and other vendors. |
| Processor | REST endpoint for structured log data. Integration with Wazuh Manager and endpoint agents. Support for Windows, Linux, and macOS. Advanced normalization and data enrichment. |
| Memory | 4 GB minimum (8-16 GB recommended) |
| Storage | 100 GB SSD (500+ GB recommended) |
| Python Runtime | Python 3.10 or later |
| Network Stability | Minimum 10 Mbps uplink |
| Inbound UDP | Port 514 (Syslog) |
| Inbound TCP | Port 8081 (API) |
| Outbound HTTPS | Port 443 (Cloud connectivity) |
Integration Stack
COMPONENT |
RECOMMENDATIONS |
|---|---|
| Infrastructure | AWS EC2 | Azure VM | Google Cloud | On-Premises |
| Database | PostgreSQL 12+ (recommended) or MongoDB |
| AI Model | Groq API (recommended) | Ollama | OpenAI-compatible |
| Notifications | Telegram | Slack | Discord | Email SMTP |
| Python Runtime | Python 3.10 or later |
Key Benefits
- Active Defense Architecture: Transitions from passive monitoring to active threat intelligence distribution
- Universal Multi-Industry Solution: Equally effective for healthcare, education, e-commerce, hosting, and enterprise sectors
- AI Forensic Intelligence: Transforms raw logs into actionable recommendations in seconds
- Zero-Day Detection: ML algorithms identify behavioral anomalies missed by signature-based firewalls
- Alert Fatigue Elimination: Consolidates thousands of duplicate alerts into actionable incident tickets
- Fixed Cost Model: Predictable budgeting without volume-based pricing fluctuations
- Comprehensive Compliance: Supports ISO 27001, UU PDP, PCI-DSS, HIPAA, and SOC2 requirements
Ready to Implement Active Defense?
Contact our team for a demonstration customized to your industry and security requirements.